OFAC sanctions screening is the continuous, risk based process of checking customers, counterparties, and transactions against the Specially Designated Nationals list and OFAC’s other consolidated sanctions lists. U.S. institutions are expected to pull directly from official OFAC data, not third party summaries, and to run that check on an ongoing basis rather than once at onboarding. The practical move: build a program around the Sanctions List Search tool, the Sanctions List Service data feeds, and the SDN list itself, then document every decision you make on a hit.
TL;DR:
- Continuous OFAC sanctions screening must include up-to-date, official data feeds rather than relying on manual checks or third-party summaries.
- Name matches should be paired with secondary identifiers like date of birth or passport number; a name-only hit requires investigation, not immediate action.
- A robust compliance program involves management commitment, risk assessment, internal controls, independent testing, and specific training, especially for UBO mapping.
- Proper investigation of a sanctions hit follows a five-step process, emphasizing documentation and legal consultation before escalating or blocking transactions.
- Automated screening tools should be supplemented by thorough record-keeping and layered due diligence, especially for complex corporate ownership structures.
Table of Contents
- How OFAC Name Matching Actually Works
- The Five Components Of A Risk-Based OFAC Compliance Program
- Investigating A Sanctions Hit: A Five-Step Checklist
- Choosing Screening Technology: Manual Lookups Versus Automated Engines
- What A Compliance-Focused Banking Partner Adds To Sanctions Screening
- What Happens When Sanctions Screening Fails
- Keeping Screening Data Accurate As Lists Change
- Connecting OFAC Screening To Your Wider AML And KYC Program
- Where OFAC Screening Still Falls Short
- What Actually Separates A Working Program From A Paper One
- How Prominencebank Supports OFAC-Aware Account Onboarding
- Sources
- FAQ
How OFAC Name Matching Actually Works
Fuzzy matching exists because sanctioned names rarely show up the way they appear on the SDN list. Transliteration from Arabic, Cyrillic, or Chinese scripts produces multiple spellings for the same person, and cultural naming conventions (patronymics, compound surnames, honorifics) create false negatives if your algorithm is too literal.
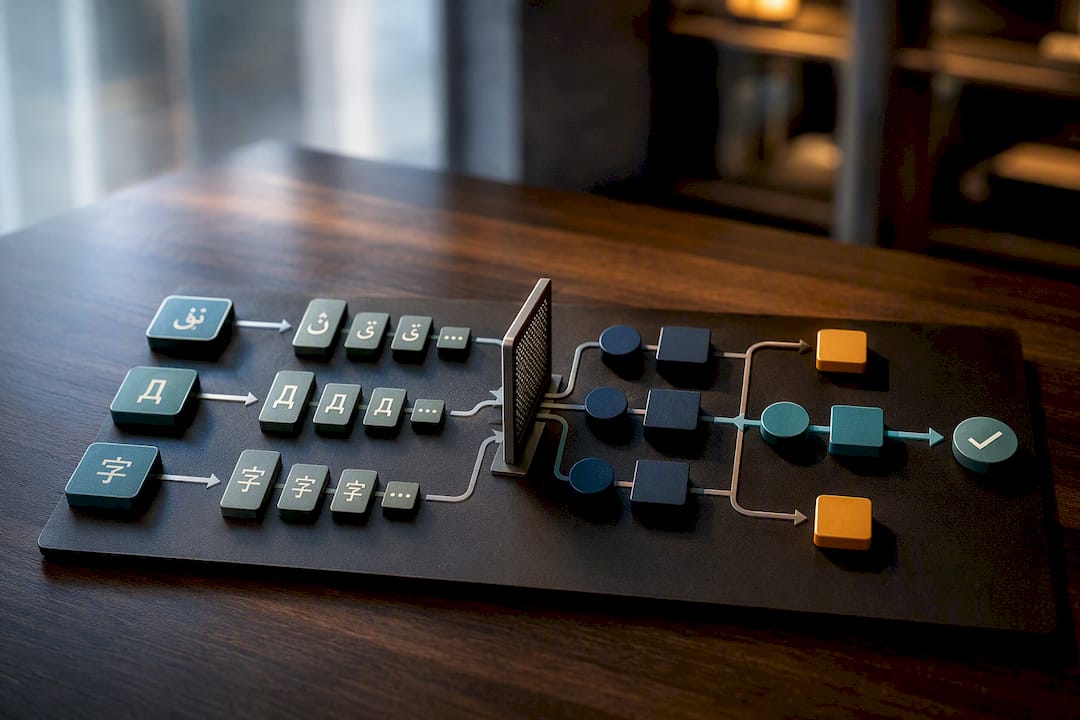
That’s why secondary identifiers carry so much weight. A name match alone tells you almost nothing; a name match paired with a date of birth, passport number, BIC/SWIFT code, or Legal Entity Identifier tells you a lot more.
Monitoring cadence should track activity type:
- Onboarding: full screen against SDN and consolidated lists before account opening.
- Transaction flows: real time or near real time screening on every wire, especially cross-border payments.
- UBO refresh: periodic re-screening of beneficial owners, since ownership structures shift and sanctions lists update constantly.
Pro Tip: Treat a name-only match as a lead, not a conclusion. The OFAC FAQs on assessing name matches are explicit that a hit should trigger investigation, not an automatic block.
The Five Components Of A Risk-Based OFAC Compliance Program
OFAC’s own Framework for OFAC Compliance Commitments lays out five components regulators expect to see, and OFAC has said it may weigh an effective program favorably when assessing enforcement outcomes.
- Management commitment. Senior leadership needs to fund the program, empower the compliance officer, and treat sanctions risk as a business priority, not a checkbox.
- Risk assessment. Map your actual exposure across clients, products, geographies, and intermediary relationships. A domestic retail bank and a correspondent bank handling wire transfers from six countries carry very different risk profiles.
- Internal controls. This is where list-refresh procedures, segmented risk scoring thresholds, and escalation paths live. Higher-risk segments (correspondent banking, cross-border trade finance) should carry tighter thresholds than low-risk retail accounts.
- Testing and auditing. Independent testing, meaning someone outside the screening function reviews it, catches the gaps day to day operators miss: stale filters, missed program codes, undocumented overrides.
- Training. Front-line staff and compliance analysts need role-specific training, not a single annual slideshow everyone clicks through.
When you scope the risk assessment, don’t stop at the named account holder. Ultimate beneficial ownership mapping matters just as much for corporate clients with layered ownership, since a sanctioned individual can sit two or three tiers behind a clean-looking holding company.
A related resource on online bank compliance for high-net-worth clients walks through how that ownership mapping plays out in practice for complex account structures.
Investigating A Sanctions Hit: A Five-Step Checklist
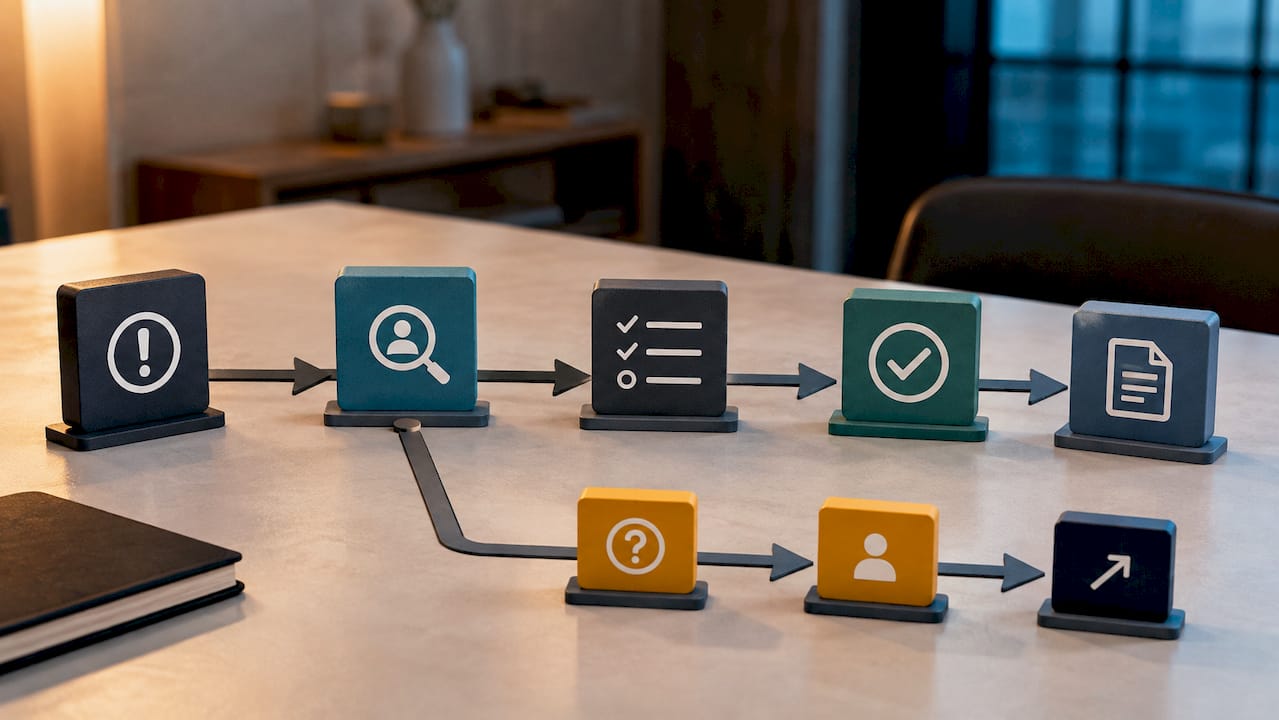
A hit is not a violation. It’s a trigger for a documented investigation, and OFAC’s own guidance lays out roughly this sequence:
- Identify the list and program code. Confirm whether the match came from the SDN list or a sectoral program, since the restrictions differ.
- Compare all available identifiers. Name, date of birth, address, nationality, and any government ID against the SDN entry.
- Collect missing information. Request additional documentation from the client or counterparty if identifiers are incomplete.
- Escalate or block if warranted. If the match holds up, freeze the transaction or account and notify OFAC as required.
- Document the rationale. Write down exactly why you cleared or escalated the hit, even when the answer is obvious to you.
That last step is the one auditors care about most. A defensible file explaining why a near-miss was not escalated matters as much as the screening technology itself.
Pro Tip: Log every near-miss review, even the ones you clear in thirty seconds. Examiners read the absence of documentation as an absence of oversight, not as evidence the case was easy.
When a match is ambiguous or the client has genuine sanctions exposure, loop in legal counsel before you act. Record the date of escalation, who was consulted, and the outcome.
Choosing Screening Technology: Manual Lookups Versus Automated Engines
A manual search on the Sanctions List Search tool works for occasional checks. It breaks down the moment you’re screening a payment batch, an onboarding queue with hundreds of applicants, or a book of correspondent accounts. At that scale, you need list ingestion that runs on a schedule and a screening engine that can hold configurable thresholds.
Three integration points matter most:
- Onboarding KYC, where new client names and UBOs get screened before an account opens.
- Payment screening, covering SWIFT and ISO 20022 message fields, which is a fundamentally different exercise than name screening a client roster since it runs against live transaction data in near real time.
- Ongoing UBO monitoring, catching ownership changes that occur after the account is already active.
When evaluating a vendor or building in-house, look for daily list refreshes pulled from the Sanctions List Service, name-science handling for transliteration variants, secondary-identifier scoring, full audit logs, and configurable thresholds by risk segment. Institutions running meaningful volume are generally expected to have moved past spreadsheet-based manual checks entirely.
What A Compliance-Focused Banking Partner Adds To Sanctions Screening
Prominencebank builds sanctions-aware controls directly into onboarding for multi-currency business accounts, corporate structures, and private client relationships. That means UBO mapping happens before an account opens, not after a regulator asks for it, and escalation channels exist so unusual matches get a documented second look rather than a rubber stamp.
For complex corporate clients with layered ownership, that first-hand structuring experience helps identify where concealed exposure tends to hide. It’s the same principle covered in the guide to opening an offshore bank account, where documentation depth at intake determines how smooth screening runs later.
What Happens When Sanctions Screening Fails
Non-compliance with OFAC sanctions requirements carries civil and criminal exposure, and OFAC enforces under strict liability. That means a violation can occur even without intent, though willfulness dramatically increases the penalty and the likelihood of criminal referral.
Civil penalties are calculated per violation and can scale into the millions of dollars for institutions handling high transaction volumes, since each processed payment or serviced account tied to a sanctioned party can count separately. Criminal penalties apply where the government can show willful violations, and those cases carry the possibility of imprisonment for responsible individuals, not just fines against the institution.
Beyond the direct penalty, OFAC settlements typically come with consent orders requiring remediation: independent monitors, enhanced reporting to OFAC, and mandated program overhauls. The reputational cost often outlasts the financial one. A bank named in an OFAC enforcement action faces correspondent banking relationships that get reviewed or severed, and counterparties that quietly route around it going forward.
OFAC has also been clear that having an effective sanctions compliance program in place at the time of a violation can factor into how it calculates penalties. That’s the practical argument for building the five-component framework properly rather than treating it as paperwork: it’s the difference between a fine that’s painful and one that’s existential. Root causes in past enforcement actions consistently trace back to outdated screening filters and incomplete due diligence, not exotic sanctions-evasion schemes.
Keeping Screening Data Accurate As Lists Change
Sanctions lists change more often than most compliance calendars assume. OFAC adds designations, delists individuals following successful appeals, and updates program codes on a rolling basis, sometimes several times in a single week during periods of geopolitical escalation.
The baseline discipline is subscribing to OFAC’s update alerts and pulling from the Sanctions List Service data files rather than a cached or third-party copy that might lag behind the official release. Archived delta files let you verify exactly what changed between refreshes, which matters when an auditor asks why a name wasn’t flagged last month but is flagged today.
A few habits separate teams with clean data from teams fighting fires:
- Automate the refresh. Manual downloads introduce human delay; a scheduled pull removes it.
- Version your data. Keep a record of which list version was active on the date of every screening decision.
- Reconcile regularly. Spot-check your internal list against OFAC’s published version monthly, not just when something looks wrong.
- Segment your thresholds. Retail onboarding and correspondent payment screening carry different risk profiles and should use different match sensitivity settings, with review logs showing why each threshold was set where it is.
Getting this wrong doesn’t usually look dramatic. It looks like a name that should have matched three weeks ago quietly slipping through because someone forgot to re-index after a data pull.
Connecting OFAC Screening To Your Wider AML And KYC Program
Sanctions screening works best as one module inside a broader AML and KYC program rather than a bolted-on side process. The same customer due diligence data you collect for AML purposes (identity verification, source of funds, beneficial ownership) is exactly what a sanctions investigator needs to resolve a hit quickly.
Institutions that run sanctions screening as an isolated function tend to duplicate data collection: KYC analysts gather one set of documents, sanctions analysts request overlapping documents separately, and the client experience suffers while nothing gets faster. Folding sanctions screening into the same case management system used for suspicious activity monitoring means an analyst investigating a hit already has transaction history, prior SAR filings, and UBO data in front of them.
This also strengthens your risk assessment. A comprehensive international banking compliance approach treats sanctions exposure, AML risk, and KYC depth as inputs to the same client risk score, rather than three separate scores that never talk to each other. For businesses with foreign ownership stakes, the overlap gets even tighter. Regulatory expectations around foreign ownership disclosure in lending echo the same UBO transparency principles that drive sanctions risk assessments.
Where OFAC Screening Still Falls Short
False positives are the daily tax every screening program pays. Common names, transliteration variants, and generic corporate names generate matches that consume analyst time without ever surfacing a real sanctioned party. A bank running thousands of daily transactions can generate hundreds of alerts that need human review, and most of them resolve to nothing.
Data latency is the quieter problem. Even with automated ingestion from the Sanctions List Service, there’s a gap between when OFAC publishes an update and when your system reflects it, especially if your refresh cycle runs on a schedule rather than triggering on publication. During a fast-moving sanctions event, that gap can matter.
Name-only matching remains a structural limitation too. Two people can share a name and nationality without being remotely related, and a screening engine without strong secondary-identifier scoring will treat both cases identically. Layered corporate ownership compounds this: a shell company two tiers removed from a sanctioned individual can pass a surface-level name screen cleanly while still carrying real exposure.
None of this argues against automated screening. It argues for treating the technology as one layer in a system that also includes trained analysts, secondary identifiers, and UBO mapping deep enough to catch what name matching alone misses.
What Actually Separates A Working Program From A Paper One
Most guidance on this topic treats OFAC screening as a technology problem: pick the right vendor, tune the algorithm, done. That’s backwards. The programs that hold up under enforcement scrutiny are the ones with a documented rationale behind every disposition, not the ones with the fanciest matching algorithm.
The conventional advice underweights one thing badly: UBO depth. Plenty of institutions screen the named account holder flawlessly and never look past the second layer of corporate ownership. That’s exactly where sanctioned exposure tends to hide, because anyone trying to evade sanctions knows the first layer gets checked.
If you take one thing from this guide, prioritize the documentation habit over the technology purchase. A mid-tier screening engine with rigorous, logged investigator decisions will outperform a top-tier engine with sloppy files, every time an examiner shows up. Get the five-component framework genuinely operational first. The software upgrade can come second.
— Harold
How Prominencebank Supports OFAC-Aware Account Onboarding
Opening a multi-currency account or a complex corporate structure shouldn’t mean starting your sanctions documentation from scratch every time. Prominencebank builds enhanced due diligence and UBO mapping into account opening itself, so the ownership and identifier data your screening program needs is already documented before the account goes live, not chased down after a hit forces the question.
For international businesses and high-net-worth clients managing layered structures, that means fewer surprises during a periodic re-screen and a documented trail ready for your own compliance file. Prominencebank’s multi-currency account setup pairs with corporate banking solutions built for complex ownership structures, giving your compliance team a partner that already thinks in terms of beneficial ownership and escalation paths. If your program needs a banking relationship that treats sanctions-aware documentation as standard practice rather than an add-on, get in touch with Prominencebank to discuss account setup for your structure.
Sources
Most compliance teams start with the Sanctions List Search tool, a free public interface that lets you type a name and get back approximate matches using fuzzy logic. It’s fine for a one-off check on a walk-in client or a quick second look during an investigation. It is not built to screen a large payment file overnight.
For that volume, OFAC points institutions toward the Sanctions List Service, which publishes the SDN list and consolidated list as downloadable XML, CSV, and JSON files designed for automated ingestion. A few things matter here:
- Sanctions List Search
Skipping the data files and relying on manual lookups is the single most common gap examiners flag during reviews.
FAQ
Is OFAC screening required?
Yes. U.S. financial institutions and many businesses are legally required to screen against OFAC’s sanctions lists, and OFAC enforces this under strict liability regardless of intent.
What is the U.S. OFAC sanctions list?
The primary list is the Specially Designated Nationals and Blocked Persons list, which OFAC supplements with a broader consolidated list covering sectoral and other sanctions programs.
Which companies offer sanctions screening services?
Screening tools range from OFAC’s own free Sanctions List Search and Sanctions List Service data files to commercial screening engines; banking partners like Prominencebank also build sanctions-aware due diligence directly into account onboarding.
Can a U.S. citizen be sanctioned by OFAC?
Yes, U.S. citizens can be added to the SDN list if they meet OFAC’s designation criteria, and all U.S. persons remain subject to OFAC’s regulations regardless of who they transact with.